Quiz · Medium
Test your knowledge of encryption, hashing, keys and signatures, Kerberos, OAuth, MFA and access control models.
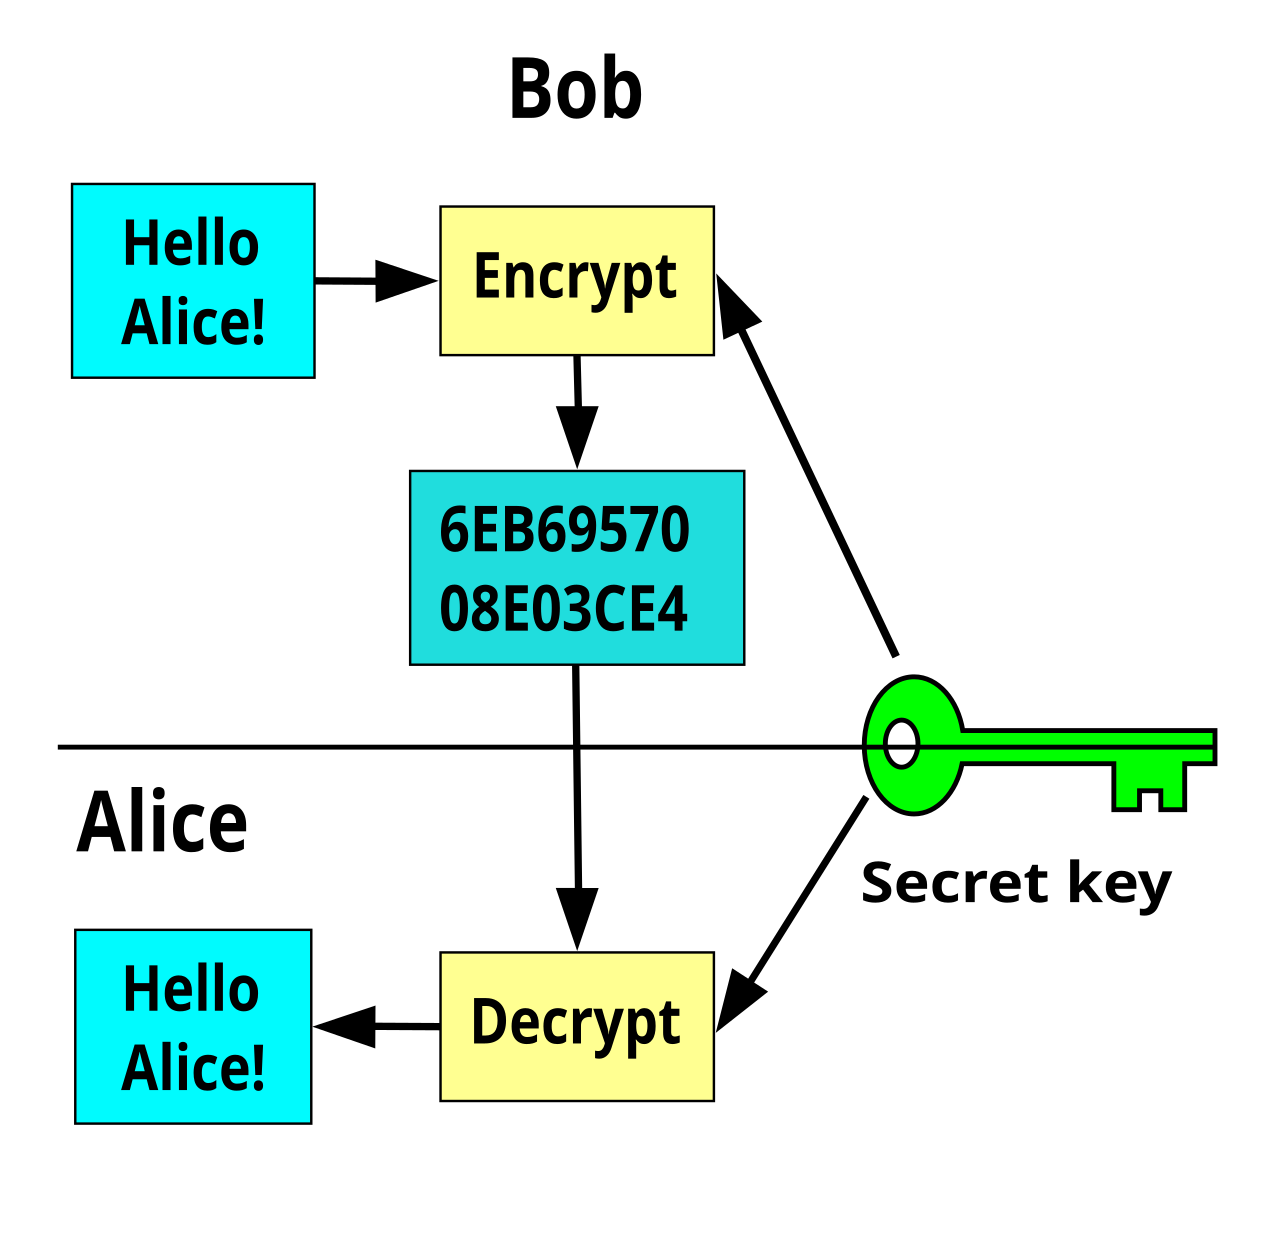
The diagram shows Bob and Alice using one shared secret key. What type of encryption is this?
Asymmetric encryption
Symmetric encryption
Hashing
Digital signature
The same key encrypts and decrypts. The challenge is sharing that key securely, which is why symmetric ciphers are often paired with key exchange such as Diffie-Hellman.
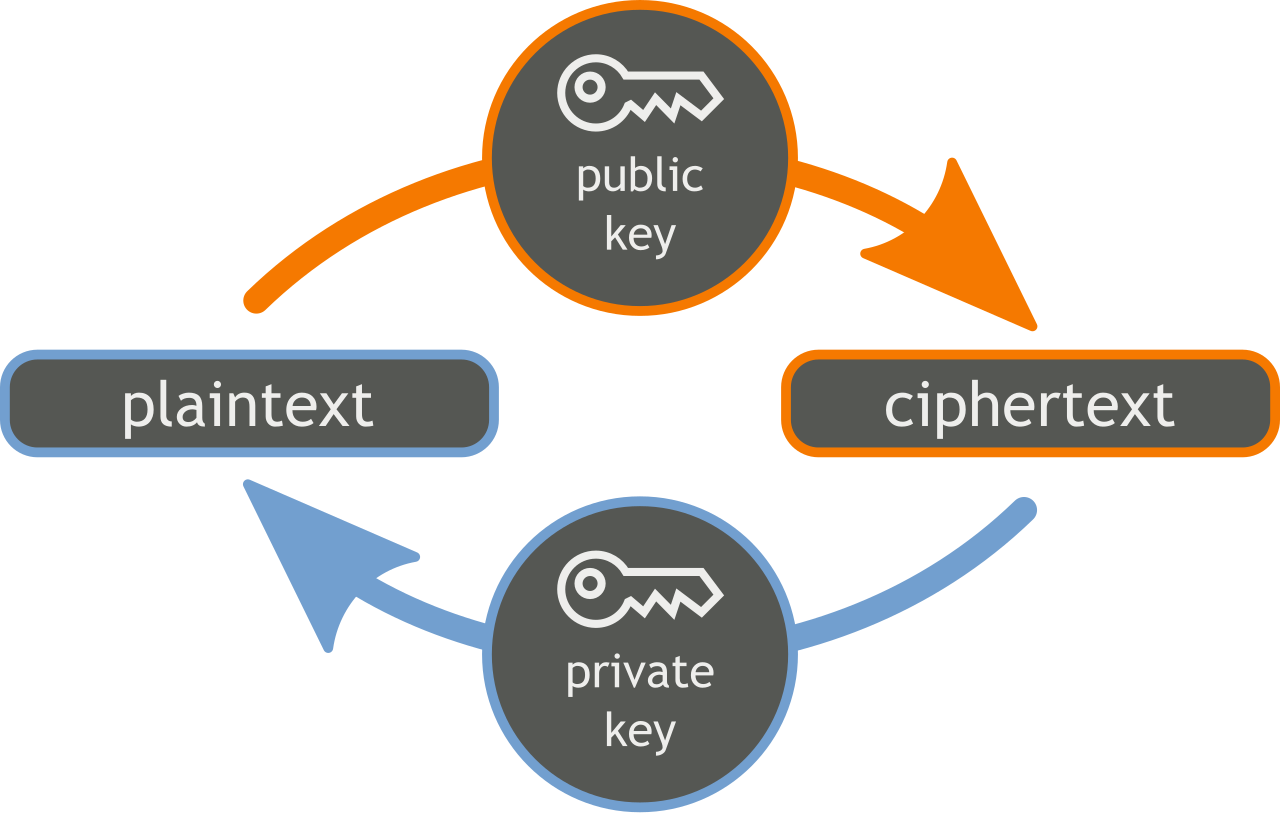
In the public-key diagram, which key must Alice keep secret?
The private key
The public key
The ciphertext
The session key
The public key can be shared with anyone for encryption; only the private key decrypts and must remain secret.
Which key does Bob use to send Alice a confidential message with RSA?
Alice's private key
Bob's private key
Bob's public key
Alice's public key
Encrypt with the recipient's public key so only the recipient's private key can decrypt. Bob's private key would be used to sign, not to protect confidentiality.
A message is signed to prove who sent it. Which key creates the signature?
The sender's public key
The recipient's public key
The sender's private key
The recipient's private key
Only the sender holds their private key, so a signature that verifies with the sender's public key proves origin and integrity (non-repudiation).
Which algorithm is the current standard for symmetric encryption of data?
DES
AES
RSA
MD5
AES (128-bit block, 128/192/256-bit keys) replaced DES. RSA is asymmetric and MD5 is a hash function.
Which cipher mode is considered unsafe because identical plaintext blocks produce identical ciphertext blocks?
ECB
CBC
GCM
CTR
ECB encrypts every block independently and leaks patterns. CBC, CTR and GCM chain or randomize blocks with an IV or counter.
Which of these should be used to store user passwords in a database?
SHA-256 without a salt
AES-256 with a shared key
Base64 encoding
bcrypt or Argon2 with a unique salt
Password storage needs a slow, salted hash. Plain SHA-256 is too fast to brute-force safely, AES is reversible if the key leaks and Base64 is not security.
What does a salt prevent?
Man-in-the-middle attacks
Phishing
Precomputed rainbow-table attacks and identical hashes for identical passwords
Replay attacks
A unique random salt per password makes precomputed tables useless and hides which users share a password.
Perfect forward secrecy ensures that...
the server certificate never expires
stealing the server's long-term key does not expose past sessions
passwords are hashed twice
all traffic is routed through a VPN
PFS uses ephemeral key exchange (ECDHE) per session, so recorded traffic stays encrypted even if the long-term private key is later compromised.
Which protocol checks whether a certificate has been revoked in real time?
OCSP
CSR
SAML
IKE
OCSP answers revocation status for a single certificate. A CSR requests a certificate and IKE negotiates IPsec keys.
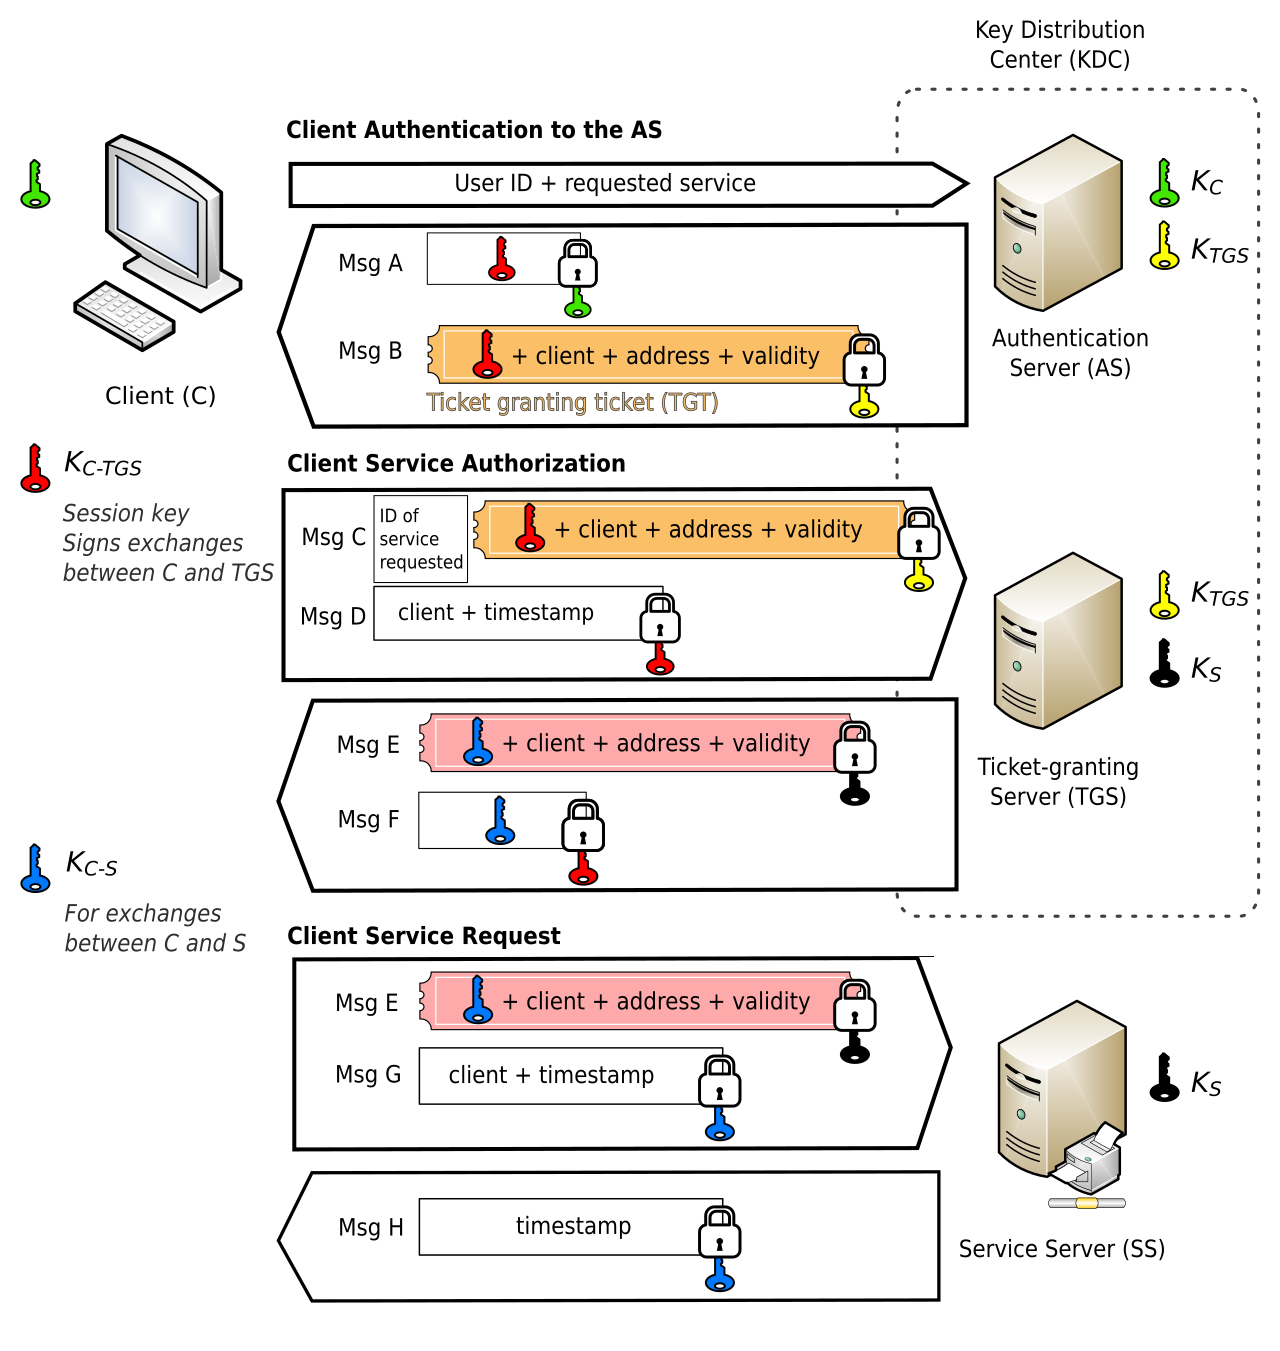
In the Kerberos diagram, what does the client receive first from the Authentication Server?
A service ticket for the file server
The service server's secret key
A SAML assertion
A Ticket Granting Ticket (TGT)
The AS issues the TGT; the client then presents it to the TGS to request service tickets. The service server's key never goes to the client.
Image: Jeran Renz, CC BY-SA 4.0, via Wikimedia Commons.
Kerberos authentication suddenly fails for all clients after a server's clock drifts by 20 minutes. Why?
The TGT was encrypted with the wrong cipher
The port 88 is closed by default
Kerberos tolerates only a small time skew (about 5 minutes) between hosts
The password expired
Tickets include timestamps to prevent replay; too much skew makes them invalid. Time synchronization (NTP) is essential in Active Directory.
Which protocol provides authentication, authorization and accounting by encrypting the entire payload and using TCP?
RADIUS
TACACS+
LDAP
SNMPv1
TACACS+ (TCP 49) encrypts the whole packet and separates AAA. RADIUS (UDP) encrypts only the password field.
A web app lets a user 'Sign in with Google' so the app receives an ID token with the user's identity. Which technology provides this authentication layer?
OpenID Connect
OAuth 2.0 alone
TACACS+
Kerberos
OAuth 2.0 is for delegated authorization; OpenID Connect adds identity (ID token) on top of it.
Which access control model assigns permissions based on job function?
DAC
MAC
Rule-based ACL on the router
RBAC
Role-Based Access Control grants permissions to roles, and users get roles. DAC lets owners decide and MAC uses system-enforced labels.
A fingerprint reader rejects many legitimate employees. Which metric is too high?
False acceptance rate (FAR)
Crossover error rate (CER)
False rejection rate (FRR)
Entropy
FRR measures valid users wrongly rejected. FAR measures impostors wrongly accepted.
Which MFA method is the most resistant to phishing?
SMS one-time code
FIDO2/WebAuthn security key or passkey
Email one-time code
Security questions
FIDO2 binds the credential to the real website origin, so a fake site cannot capture a usable response. SMS and email codes can be relayed to a phishing site.
Which statement about hashing is true?
A hash is one-way and always gives the same output length
A hash can be decrypted with the right key
SHA-1 is the recommended modern hash
Longer inputs produce longer hashes
Hashing is not encryption; there is no key and no decryption. SHA-1 is deprecated and output size is fixed (SHA-256 = 256 bits).
What problem does HMAC solve that a plain hash does not?
It encrypts the message
It compresses the message
It removes the need for a key
It authenticates the sender as well as checking integrity
HMAC mixes a secret key into the hash, so only someone with the key can create a valid tag.
Which attack allows an adversary to force a TLS connection to use an older, weaker protocol?
Replay attack
Smurf attack
Downgrade attack
Bluejacking
Downgrade attacks exploit backward compatibility. Disable SSL and old TLS versions to prevent them.
