Quiz · Medium
DMZ designs, IDS and IPS, SIEM, vulnerability scoring, forensics, compliance and control types.
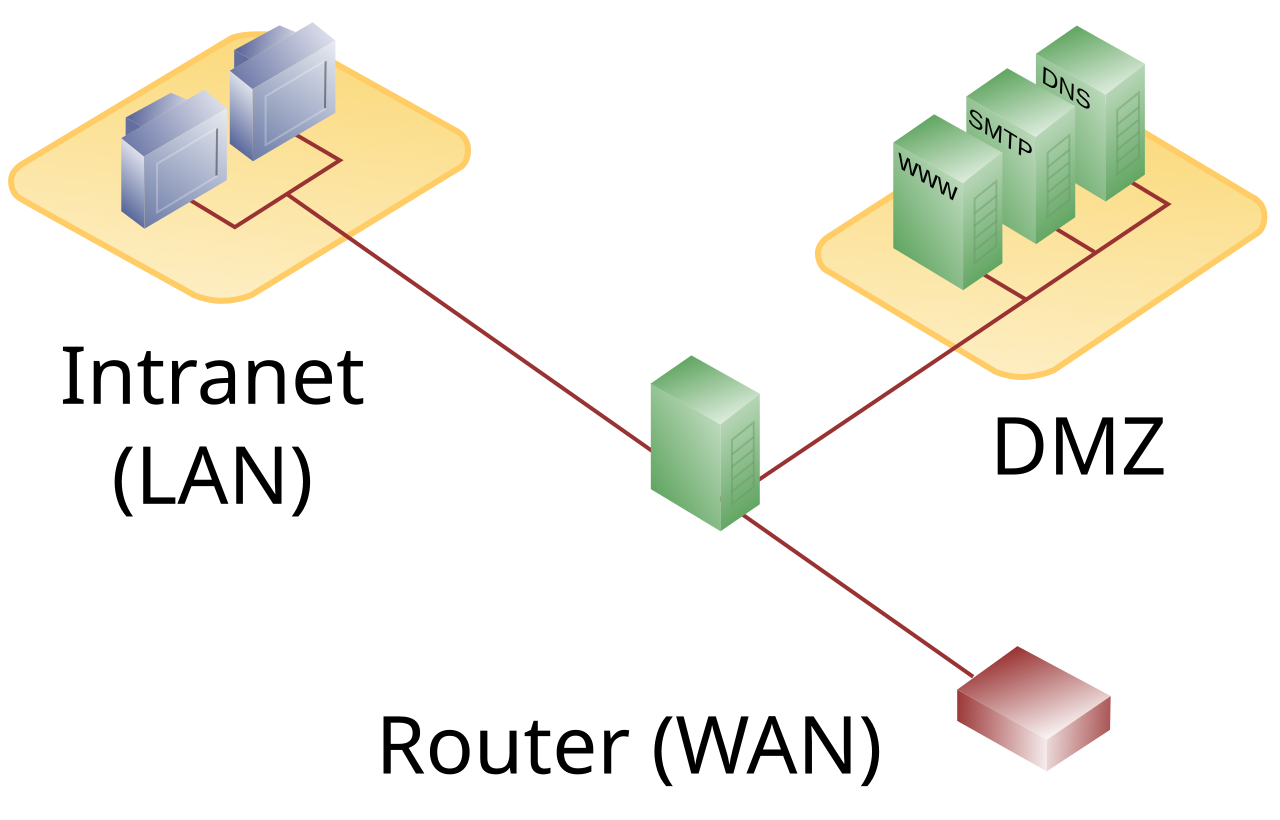
Look at the DMZ diagram with one firewall. What is the main risk of this design?
The DMZ servers cannot be reached
One compromised firewall exposes the internal LAN and the DMZ
It needs two internet connections
It cannot filter traffic
A single firewall is a single point of failure for every zone. A dual-firewall design adds another barrier.
In the dual-firewall DMZ diagram, what sits between the two firewalls?
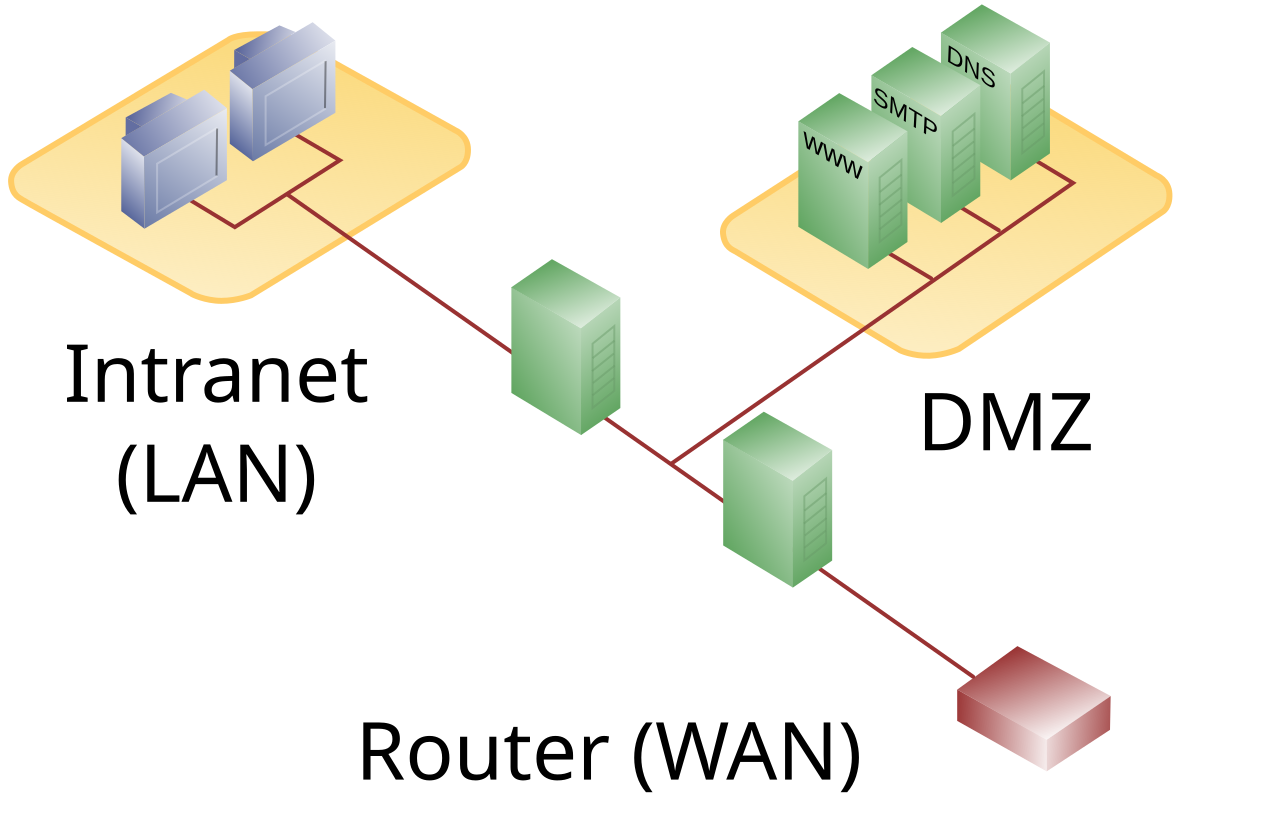
The DMZ with public-facing servers
The internal user workstations
The ISP's routers
The backup servers only
The outer firewall faces the internet, the inner firewall guards the LAN, and the DMZ hosts web, mail and DNS servers between them.
Which device sits inline and can actively block malicious traffic?
IDS
Network tap
Syslog server
IPS
An IPS is placed inline and drops or resets malicious flows. An IDS passively monitors and alerts.
A web server should be reachable from the internet but isolated from the internal network. Where should it be placed?
On the internal LAN next to the file server
On a VLAN with the domain controllers
In a DMZ (screened subnet)
Behind only the host firewall on the LAN
A DMZ limits what an attacker can reach if the public server is compromised.
Which control stops an attacker plugging a laptop into an open wall jack and getting network access?
Longer Wi-Fi passwords
802.1X port-based authentication
Disabling ICMP
Installing a honeypot
802.1X requires the device to authenticate before the switch port forwards traffic.
Which switch feature blocks rogue DHCP servers?
DHCP snooping
BPDU guard
Port mirroring
VLAN trunking
DHCP snooping allows DHCP server replies only from trusted ports.
An SOC needs to correlate logs from firewalls, servers and endpoints and raise alerts. Which tool is designed for this?
DLP
CASB
HSM
SIEM
A SIEM aggregates and correlates logs. DLP prevents data leakage, CASB governs cloud use and an HSM protects keys.
Which tool automates incident response steps such as isolating a host and blocking an IP when an alert fires?
WAF
NAC
SOAR
TPM
Security Orchestration, Automation and Response runs playbooks. A WAF filters web requests and NAC controls network admission.
Which stage of the Cyber Kill Chain comes immediately after Delivery?
Reconnaissance
Exploitation
Installation
Actions on Objectives
Order: Reconnaissance, Weaponization, Delivery, Exploitation, Installation, Command and Control, Actions on Objectives.
Which OWASP Top 10 (2021) category is first?
Broken Access Control
Injection
Cryptographic Failures
Insecure Design
A01 Broken Access Control is the top category in the 2021 list; Injection fell to A03.
A vulnerability has a CVSS base score of 9.8. How is it rated?
High
Medium
Informational only
Critical
9.0 to 10.0 is Critical, 7.0 to 8.9 High, 4.0 to 6.9 Medium and 0.1 to 3.9 Low.
A forensic investigator arrives at a running compromised server. What should be collected first?
The hard drive image
Backup tapes
Memory (RAM) contents
Printed logs
Evidence is collected in order of volatility; RAM disappears at power-off while disks and backups persist.
Which document shows who handled evidence and when?
Business impact analysis
Chain of custody
Service level agreement
Acceptable use policy
Chain of custody proves evidence integrity and admissibility.
A customer's EU personal data was breached. Under GDPR, within roughly how long must the regulator generally be notified?
72 hours
24 hours
7 days
30 days
GDPR requires notifying the supervisory authority without undue delay and where feasible within 72 hours of becoming aware.
Which regulation applies to a company that stores payment card numbers?
HIPAA
FERPA
SOX
PCI DSS
PCI DSS governs cardholder data. HIPAA covers health data, FERPA student records and SOX financial reporting.
Which type of control is a security camera?
Preventive
Corrective
Detective (physical)
Directive
Cameras record and reveal events (detective); they may also deter, but their main function is detection.
An attacker sets up a Wi-Fi network named 'CoffeeShop_Free' next to the real 'CoffeeShop' network to capture logins. What is this?
Bluesnarfing
Evil twin
War driving
Smurf attack
An evil twin imitates a legitimate SSID. Bluesnarfing uses Bluetooth and war driving is scanning for networks.
Which is the best defense against DNS cache poisoning?
DNSSEC
Disabling ICMP
Using WEP
Port security
DNSSEC signs DNS records so resolvers can verify their authenticity.
Which backup scheme restores fastest using only the last full backup plus ONE other set?
Incremental
Copy-only incremental
Snapshot of RAM
Differential
Differential backups contain all changes since the last full, so restore needs the full plus the latest differential. Incrementals require every set since the full.
True or false: a honeypot should contain real customer data to look convincing.
True
False
Honeypots must contain fake data only. Real data would put customers at risk if the honeypot is compromised.
